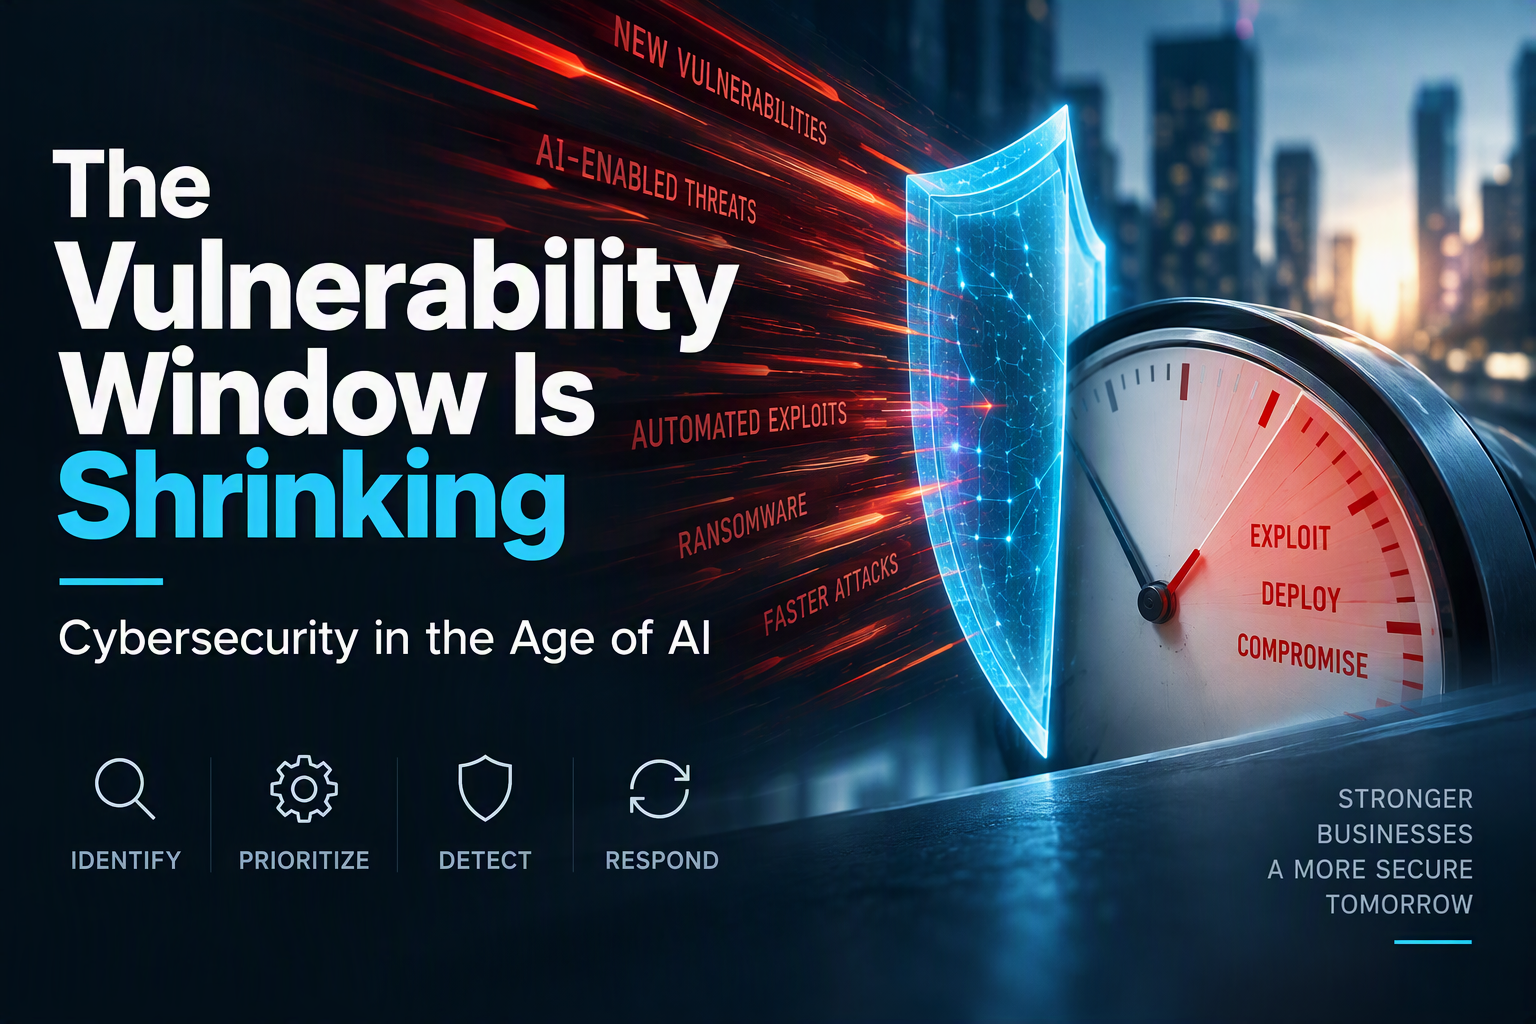


For years, cybersecurity teams have talked about a familiar race: vendors discover vulnerabilities, patches become available, businesses deploy them, and attackers try to exploit the vulnerabilities before all of that happens.
That race has changed.
Artificial Intelligence (AI) is giving both defenders and attackers capabilities that once required significant time and specialized expertise. AI can accelerate vulnerability research, reconnaissance, exploit development, social engineering, and other stages of the modern attack framework. The result is not necessarily an entirely new form of cybercrime. Rather, it's something arguably more challenging: the same attacks businesses have faced for years can now happen faster, at greater scale, and with increasing automation.
Finding and eventually patching vulnerabilities is no longer enough. We need to reduce the time between discovering risk, understanding its relevance, and taking action. Perhaps most important, however, is detecting attempted exploitation as this timeline compression hastens.
Vulnerability Management has
Become a Race Against Time
Not every vulnerability represents the same risk.
A critical vulnerability on an isolated internal system may represent a different level of urgency than a vulnerability actively being exploited against an internet-facing firewall, VPN, or application. Effective vulnerability management therefore requires more than simply looking at a CVSS score and working from highest to lowest.
There are several items that today's organizations should consider:
- Is the vulnerability being actively exploited?
- Is the affected system exposed to the Internet?
- What privileges or access could exploitation provide?
- Are exploits readily available?
- What business functions depend on the affected system?
- Is there evidence suggesting the system may already have been targeted?
- What mitigating controls exist if an immediate patch is not possible?
That philosophy increasingly aligns with guidance from the Cybersecurity and Infrastructure Security Agency (CISA) Known Exploited Vulnerabilities (KEV) Catalog. CISA specifically recommends organizations use its KEV catalog as an input to vulnerability-management prioritization rather than treating every vulnerability based solely on its published CVSS score.
Recent CISA guidance goes a step further by emphasizing rapid remediation of actively exploited vulnerabilities on exposed systems and, for certain higher-risk situations, considering whether compromise occurred before the patch was installed.
That last point is critical.
Patching closes the vulnerability. It does not necessarily remove an attacker who exploited it yesterday.
Vulnerability Management and
Threat Detection Must Converge
This is why modern cybersecurity cannot operate as a series of disconnected activities.
-
Vulnerability management tells us where we may be exposed.
-
Threat intelligence tells us what attackers are actively targeting.
-
Endpoint, identity, network, and cloud telemetry tell us what is actually happening in the environment.
-
Security operations provide the ability to investigate and respond when those signals indicate a potential compromise.
When these capabilities work together, security teams can make better decisions much faster.
AI Raises the Stakes, but the
Fundamentals Still Matter
It is tempting to think AI requires businesses to reinvent cybersecurity completely. In reality, AI makes getting the fundamentals right even more important.
The foundations remain familiar:
Know what you have.
Maintain visibility into devices, applications, cloud services, identities, and Internet-facing assets.
Continuously identify vulnerabilities.
Regular scanning and exposure management are increasingly important because the environment and threat landscape change constantly.
Prioritize based on risk.
Combine vulnerability severity with exploit intelligence, asset exposure, business criticality, and real-world threat activity.
Patch intelligently.
The goal is not merely a high patch-compliance percentage. It is reducing the window in which the vulnerabilities most likely to result in compromise remain exploitable.
Detect what prevention misses.
Endpoint Detection and Response (EDR), Identity Threat Detection and Response (ITDR), and Managed Detection and Response (MDR) provide critical visibility when preventive controls fail.
Be prepared to respond.
Organizations need well-defined escalation, containment, recovery, and incident-response processes before the incident occurs.
Where an MSP Fits
For many small and midsized businesses, doing all of this internally is not only difficult. It's nearly impossible.
Cybersecurity now requires organizations to monitor a constantly changing combination of vulnerabilities, vendor advisories, threat intelligence, endpoint activity, cloud services, identities, network infrastructure, and security alerts. It also requires people with the expertise to distinguish routine security noise from something requiring immediate action.
That is where a mature Managed Service Provider and security partner can have significant value.
At Systems Engineering, our approach combines capabilities including vulnerability management, patch management, EDR, ITDR, MDR, security operations, identity and access security, incident response support, and risk management. Our security operations capabilities extend across endpoints, network infrastructure, Microsoft 365, Azure, and other cloud services, with escalation and response processes designed to support organizations when serious threats are identified.
That integrated model matters because today's security problem isn't simply:
"Are we patched?"
The more important questions are:
"Where are we exposed? Which exposures matter most? Are attackers targeting them? Can we detect exploitation? And can we respond quickly enough if something happens?"
Those are questions that require technology, threat intelligence, process, and human expertise working together.
Cybersecurity Is Becoming a
Continuous Discipline
The lesson of today's AI-enabled threat environment isn't that businesses are powerless against increasingly sophisticated adversaries.
It is that time matters more than ever.
The organizations best positioned to manage cyber risk will be those that shorten the cycle between discovery and action: continuously understanding their exposure, prioritizing the vulnerabilities that attackers are most likely to exploit, remediating them quickly, monitoring for signs of compromise, and having people ready to respond when something gets through.
Technology can automate much of that process. AI will increasingly make both sides faster. However, cybersecurity still ultimately depends on something very human: making the right decision, about the right risk, at the right time.
For businesses looking for the right partner to support all of those capabilities, the right MSP can provide the technology, visibility, expertise, and operational capacity necessary to turn cybersecurity from a collection of tools into a continuously managed program.
At Systems Engineering, that is the role we believe a modern technology and security partner should play.
Contact us today about how our service offerings converge these cybersecurity program requirements into a package that fits any organization's needs.